Why Record-Breaking Crypto Hacks Signal a Shift Toward Infrastructure Risk
Key Takeaways
While the volume of smart contract exploits continues to rise, the most catastrophic financial losses in the crypto space are increasingly stemming from systemic infrastructure failures like cross-chain bridges and oracle manipulations.
Table of Contents
The crypto world is in a weird spot: we're seeing record-high numbers of hacks, but the way these thefts happen is fundamentally changing. While news headlines often focus on the sheer volume of exploits targeting individual decentralized finance (DeFi) protocols, the true systemic threat to institutional adoption lies in the "pipes" of the ecosystem rather than just the "valves" of individual smart contracts.
Historically, the primary hurdle for crypto adoption was the prevalence of "rookie" bugs—coding errors in smart contracts that allowed attackers to drain liquidity from new projects. However, as automated auditing tools and standard security protocols have become industry standards, these localized vulnerabilities are becoming less of a catastrophic systemic risk. Instead, we are seeing a migration of threat vectors toward large-scale infrastructure components like cross-chain bridges, oracle networks, and centralized points of failure that underpin the entire DeFi ecosystem.
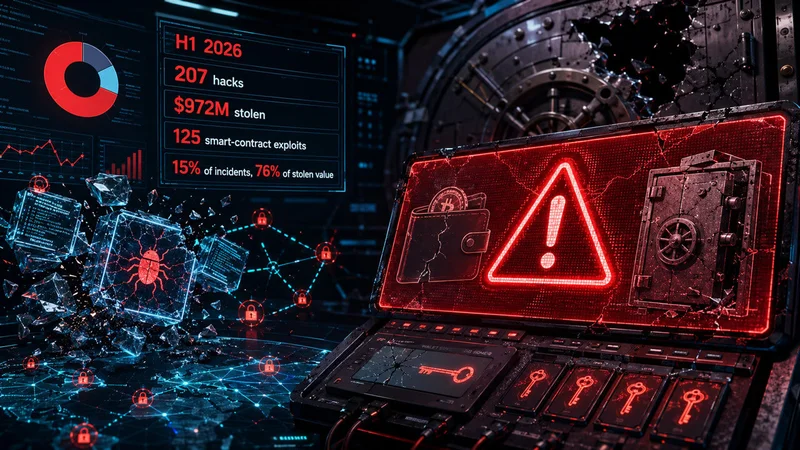
Why is the scale of theft shifting from code to infrastructure?
To understand why a breach in a cross-chain bridge causes more damage than a bug in a niche DeFi app, one must look at the complexity of multi-chain interactions. Cross-chain bridges are designed to facilitate the movement of assets between disparate blockchains. Because they rely on complex, multi-party validation mechanisms and "wrapped" asset logic, they possess an enormous attack surface. A successful breach here doesn't just affect one protocol; it can drain tens of millions of dollars across multiple chains simultaneously because the bridge serves as a critical hub for liquidity.
Similarly, oracle manipulation has emerged as a sophisticated method to bypass smart contract security entirely. Instead of attacking the code itself, actors target the data feeds that the code relies upon. By manipulating these feeds—often by targeting low-liquidity pools on decentralized exchanges—attackers can trick a protocol into accepting distorted prices, triggering massive liquidations or unfair arbitrage opportunities in a matter of seconds.
What are the primary defense mechanisms for "hardened" infrastructure?
As the risks evolve, top-tier protocols are moving past simple manual audits and adopting much stricter technical defenses. One of the most significant shifts is the adoption of formal verification. This process utilizes mathematical proofs to ensure that a contract's logic remains sound under every possible condition, virtually eliminating the "human error" element found in traditional code reviews.
Real-time monitoring systems now frequently include "circuit breakers." These are automated protocols designed to pause a contract’s functionality if it detects anomalous transaction volumes or extreme price deviations. This provides a vital layer of defense against flash-loan attacks and rapid oracle manipulations. The move toward Decentralized Infrastructure (DePIN) is aimed at removing centralized points of failure—such as single-entity key management or front-end hosting—by replacing them with decentralized sequencers and oracle networks like Chainlink.
Key Facts
- Infrastructure Dominance: While smart contract hacks are more frequent, their median financial impact is shrinking compared to infrastructure breaches (bridges, CEX security, and oracles).
- Bridge Vulnerability: Cross-chain bridges are high-value targets due to their reliance on complex multi-party validation logic.
- Oracle Tactics: Attackers target low-liquidity pools to manipulate the data feeds that govern automated price actions in DeFi.
- Formal Verification: Mathematical proof-based verification is becoming the standard for institutional-grade smart contracts.
- Circuit Breakers: Automated pauses are being implemented to stop "flash" events before they can drain total value locked (TVL).
Expert Commentary
The shift from "bug hunting" to "infrastructure hardening" stands as the most critical transition for institutional capital over the next five years. When evaluating a DeFi asset today, gas efficiency or governance models take a backseat. We're looking straight at the stability of the underlying infrastructure.
The move toward DePIN and formal verification suggests that the industry is attempting to build a "hardened" environment. For large-scale institutions, the primary concern is the systemic integrity of the bridge or the oracle providing the price data. We are moving into an era where "safety" will be synonymous with decentralized infrastructure and mathematical certainty. The protocols that survive the next cycle will be those that stop trying to hide behind manual audits and start building on a foundation of automated circuit breakers and verifiable, decentralized components. The focus is shifting from making the "valves" safer to ensuring the "pipes" cannot be hijacked.
Google Search Preference
Add Fintech Monster to your preferred sources
Never miss deep, analytical fintech insights. Prioritize our stories in your Google Search, Discover feed, and AI Overviews with one click.
About the Author
Fintech Monster
Fintech Monster is run by a solo editor with over 20 years of experience in the IT industry. A long-time tech blogger and active trader, the editor brings a combination of deep technical expertise and extended trading experience to analyze the latest fintech startups, market moves, and crypto trends.
Related Articles
Recommended
Securing the Digital Frontier: Europe’s Strategic Integration of AI and Cybersecurity
The European Union's new Action Plan integrates AI governance directly into cybersecurity protocols to protect the financial sector and digital economy from systemic risks like data poisoning and adversarial machine learning.
The $9M Black Hole: Deconstructing the Tectonic Exploit on Cronos Network
The exploit exposed critical systemic vulnerabilities in cross-chain bridge mechanisms, proving that standard ledger rollbacks are insufficient to guarantee asset recovery when pre-consensus funds are drained via protocol flaws.
$320 Million Standoff: What Does a Whitehat Exploit Reveal About Cross-Chain Security?
The standoff involving $320 million in drained BTC highlights critical systemic flaws in cross-chain bridging, demanding mandatory formal verification protocols before institutional capital can safely deploy across disparate networks.
Aave’s Emergency ‘Kill Switch’: How One-Way Governance Calls Redefine Decentralized Risk Management
A proposed Aave governance mechanism allows emergency roles to unilaterally freeze market activity during critical exploits, prioritizing immediate stability but creating a permanent risk of non-reversibility and loss of liquidity path.
Supply Chain Vulnerability: How a Logistics Breach Threatens Crypto Cold Storage Security
A data breach affecting 67,000 US customers at a third-party shipping provider highlights that operational and supply chain risks pose a more immediate threat to crypto infrastructure than core protocol vulnerabilities.